npm v12 now blocks install scripts unless you explicitly approve them. It should have been the default years ago.
What changed
preinstall, install and postinstall no longer run on their own.
That one behaviour is how a large share of supply chain attacks worked: publish a package, wait for someone to type npm install, then run whatever you like on their machine and in their CI. Install scripts run with the same permissions as the user or CI job doing the install, which is why attackers liked them so much.
It will break some builds
Some builds will break. Those are the builds that were running arbitrary code from strangers.
What to do now
Check which of your dependencies actually need a postinstall hook. It's usually fewer than you think. Approve those on purpose, and when a new dependency asks for an install script, review it before you let it through.
Building something like this?
I'm Ahmed Mamdouh, a senior full-stack and AI engineer. I reply within one working day.
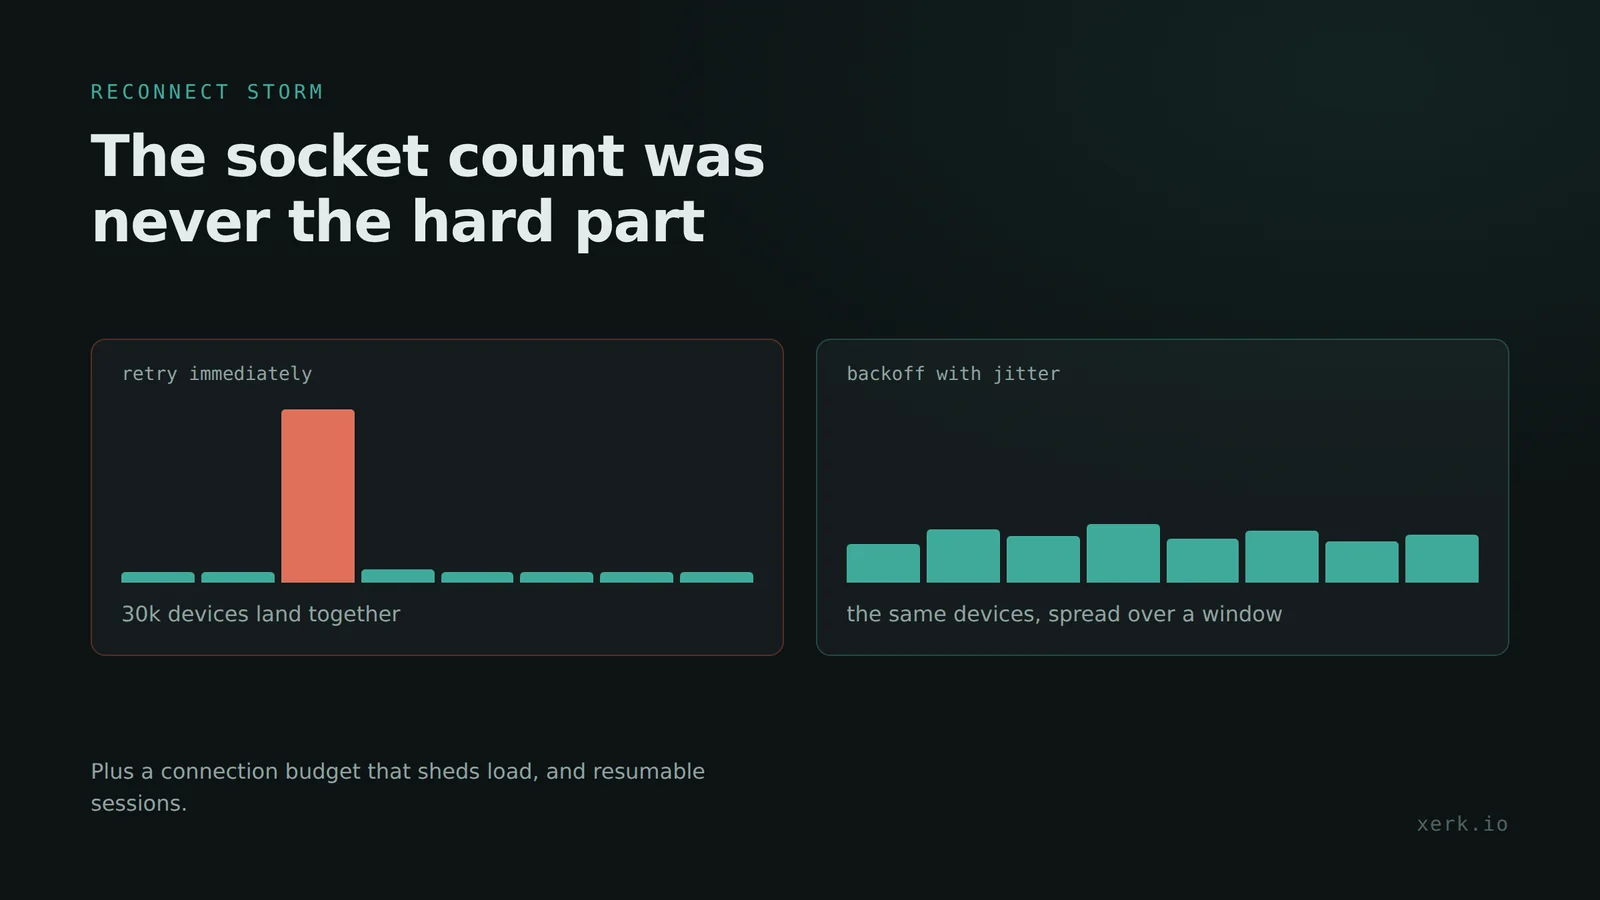
Scaling 100k WebSocket connections: the reconnect storm
At 100k+ concurrent sockets the count is easy. The reconnect storm is what breaks, and jittered backoff, load shedding and resumable sessions fix it.
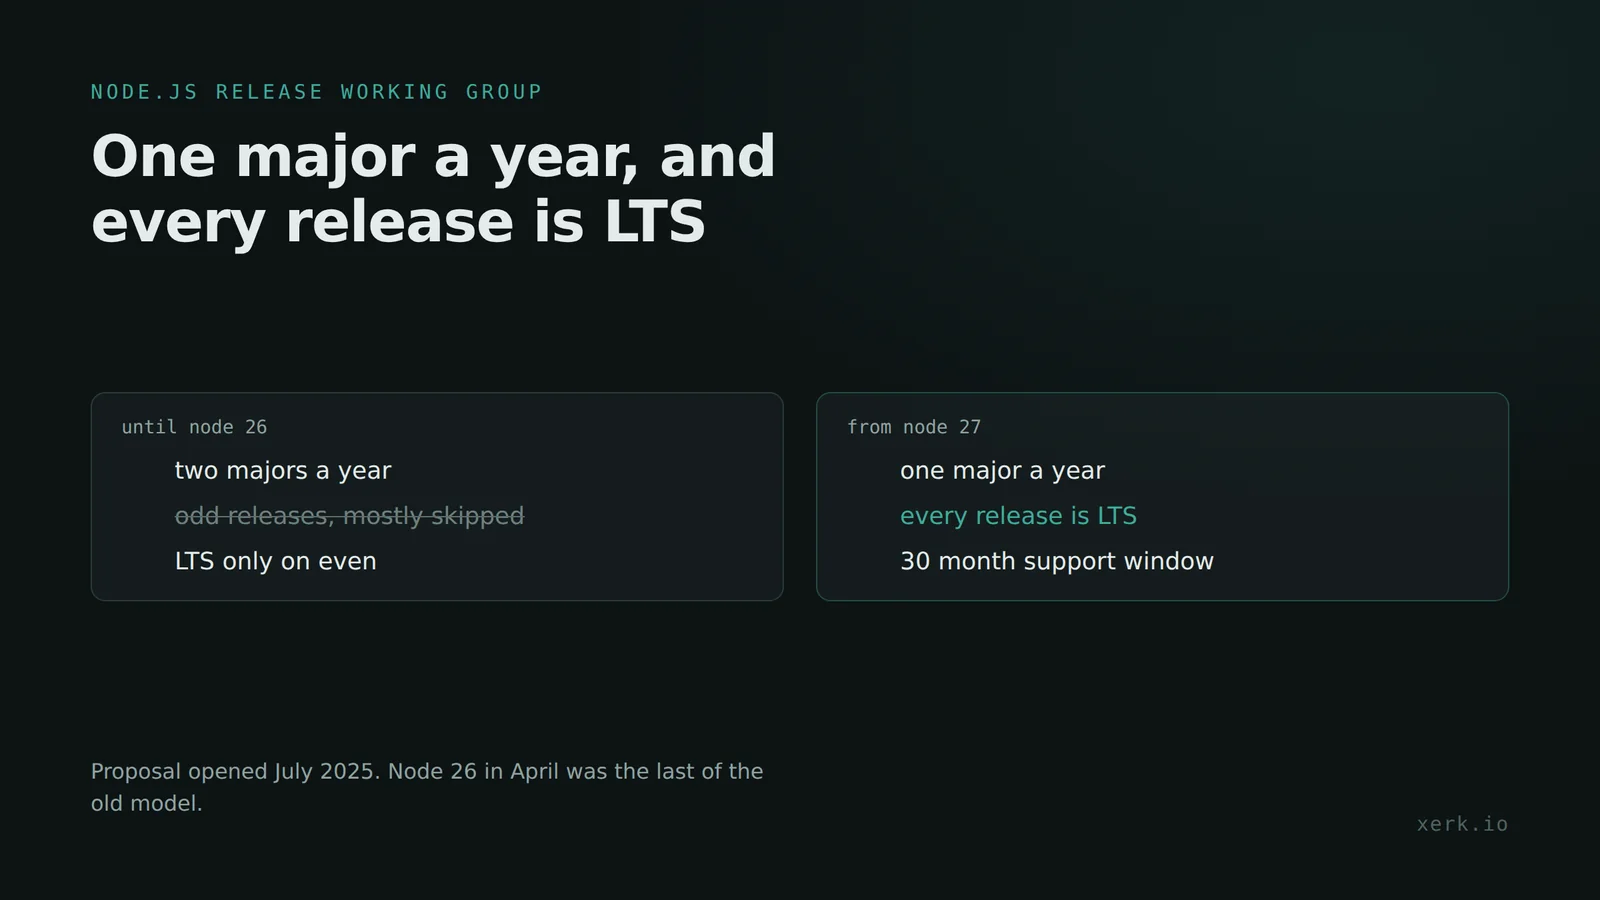
Node.js moves to one major release a year
From Node 27, Node.js ships one major a year and every release becomes LTS, ending the odd/even split most teams already ignored.
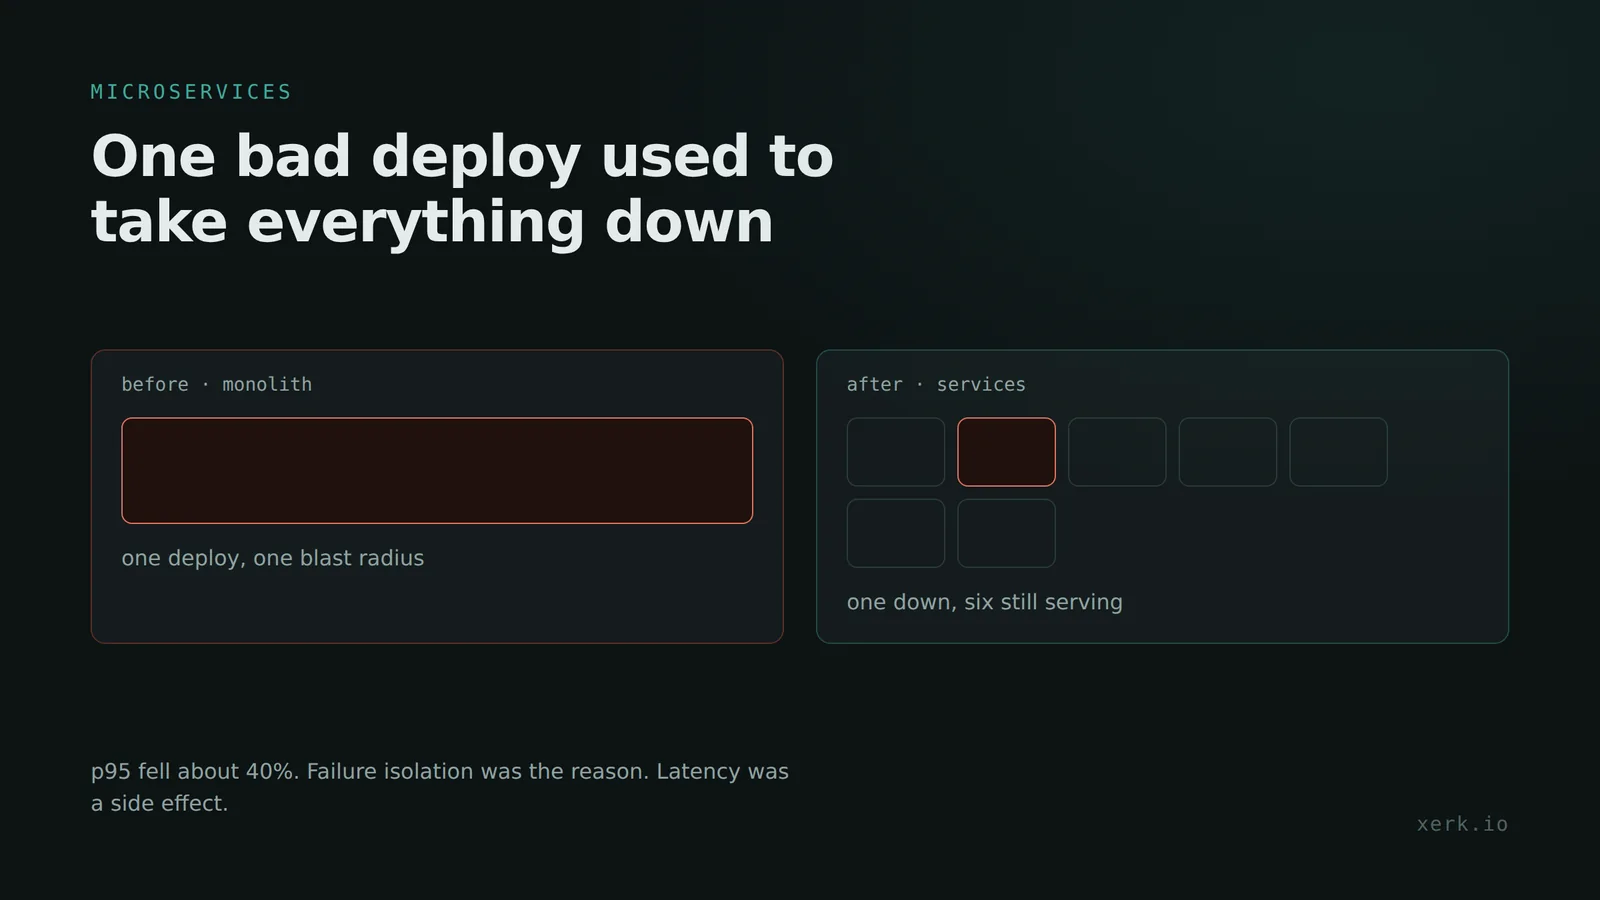
Splitting a monolith: what it actually bought us
Split a monolith for failure isolation and team ownership. If speed is the goal, profile first; the cause is usually a missing index.